
When to File a SAR
A bank files a SAR within 30 days of initial detection, or 60 days if no suspect was identified that day.
TL;DR: A risk-based approach to AML is the requirement to identify, assess, and mitigate money laundering and terrorist financing risk in proportion to that risk: enhanced measures where risk is higher, and simplified measures only where risk is lower and the rules allow it. The approach is not the written BSA/AML risk assessment. FATF's April 2022 effectiveness report found that over 80 percent of FATF member countries were substantially or highly effective on risk understanding and response, against 19 percent of FATF-style regional body members.
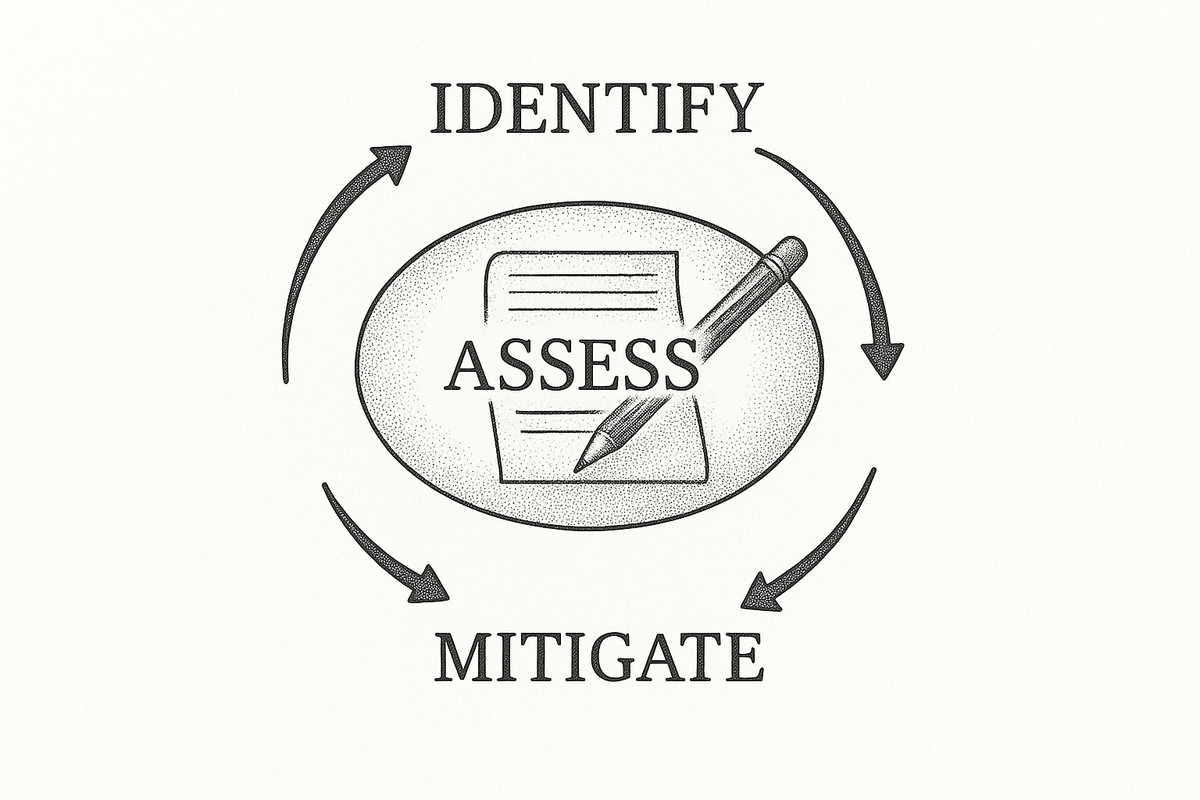
A risk-based approach to AML is the rule that preventive measures scale with money laundering and terrorist financing risk. The FATF Recommendations, last updated in June 2026, place that rule in Recommendation 1. Countries apply the approach so that measures to prevent or mitigate money laundering and terrorist financing are proportionate to the risks identified. Financial institutions have to identify, assess, and take effective action to mitigate their own risks. Higher risk calls for enhanced measures. Lower risk, where a country permits it, calls for simplified measures. The same product does not have to carry the same control at every institution, or for every customer inside one institution.
The interpretive note to Recommendation 1 sets the sequence institutions actually run. They keep processes to identify, assess, monitor, manage, and mitigate money laundering and terrorist financing risks. Senior management approves the policies, controls, and procedures. The measures, enhanced or simplified, stay proportionate to the risks identified and consistent with national requirements. One intensity for every relationship is not the approach. Dropping a control because a file was labeled low is not the approach either.
In the United States the same rule already sits inside the program regulation. 31 CFR 1020.210 requires internal controls, independent testing, a designated compliance officer, training, and risk-based procedures for ongoing customer due diligence. The five pillars of an AML compliance program are the container. The risk-based approach is how the work inside that container is sized.
The written BSA/AML risk assessment is the analysis. The risk-based approach is what the institution does after the analysis. The FFIEC BSA/AML Examination Manual says banks structure compliance programs to be risk-based, and that a written assessment, while not a specific legal requirement, is how a bank identifies money laundering, terrorist financing, and other illicit finance risks and builds internal controls to match. Documenting the assessment is sound practice. Filing the PDF and leaving the controls untouched is a different act.
The BSA/AML risk assessment covers how that document is built: products and services, customers, geographies, and delivery channels, read from inherent risk through control effectiveness to residual risk. This article does not repeat that method. The approach starts when a residual-risk conclusion changes customer due diligence, screening, monitoring, or independent testing. A conclusion that changes none of them is an assessment without an approach.
FATF's April 2022 report, drawing on mutual evaluations through December 2021, separates the document from the result. More than 90 percent of the 59 countries in its sample had completed a risk assessment by the on-site visit. On Immediate Outcome 1, which tests whether a jurisdiction understands its risks and acts on them, 3 percent of FATF member countries reached the top rating of high effectiveness. Among members of FATF-style regional bodies, 81 percent were rated low or moderate. Writing the risks down did not, by itself, produce a risk-based regime.
Four controls absorb the approach. Each one has a margin that risk is allowed to move, and a floor that risk is not allowed to remove. Institutions that treat "risk-based" as a sentence in the policy move neither.
Customer due diligence is where proportion is easiest to assert and hardest to show. Under 31 CFR 1020.210 the profile comes from the nature and purpose of the relationship, and customer information, including beneficial owners, is updated on a risk basis. Customer risk rating is how the score is produced. The approach is what the score is allowed to trigger: collection beyond the baseline, the events that force a refresh, and whether enhanced due diligence is a reviewed file or a sentence in a procedure.
FATF's interpretive note lets the intensity differ by stage. An institution can apply ordinary due diligence at acceptance and enhanced monitoring afterward, or the reverse, when the risk factors point that way. A lower rating can lengthen the refresh cycle. A higher rating can require source of funds, a closer look at ownership, and a named reviewer. The rating does not authorize the institution to skip the identification the rule already requires, and simplified measures stop being available once money laundering or terrorist financing is suspected.
Screening moves with risk at the margin. Match sensitivity, supplemental lists, the rescreening cycle, and the order in which hits are cleared can follow the book and the customer. A domestic payroll portfolio and a cross-border payments book should not share one rescreening calendar. The legal floor does not move with the label. Recommendation 1 still requires full implementation of the targeted financial sanctions in Recommendation 7 where proliferation-financing risk is assessed as lower.
Monitoring is the approach made mechanical. Under 31 CFR 1020.210, ongoing monitoring has two jobs: identify and report suspicious transactions, and, on a risk basis, keep customer information current. Thresholds, scenario coverage, and review speed are the levers. A correspondent account and a consumer checking account can sit on the same platform and still justify different scenarios and a different clock for review. A segment the assessment rates high, and that still shares the retail threshold, is a control that ignored the assessment. A wider band on a lower-risk segment is defensible when the institution can show the risk it relied on. The wider band is not a device for shrinking the queue.
Independent testing is risk-based in scope and cadence, not in whether it happens. The FFIEC manual sets no regulatory frequency. Testing should be commensurate with the institution's risk profile. The manual's example is every 12 to 18 months, with another test when the risk profile, systems, compliance staff, or processes change. AML independent testing requirements cover independence, the report, and the workpapers. A test that samples the quietest product and skips the one the assessment calls high has not followed the approach.
Simplified measures are a permission, not a discount on the legal minimum. The interpretive note to Recommendation 1 withholds them whenever there is a suspicion of money laundering or terrorist financing. Proliferation-financing risk can be assessed as lower without any relaxation of targeted financial sanctions. In the United States, the duty in 31 CFR 1020.210 to monitor for suspicious transactions and report them does not step down because a customer risk rating is low. The rating changes how much attention the relationship receives before suspicion arises. Once suspicion arises, the measure has already been selected.
Proportion runs in the other direction with the same discipline. Rating a segment high is an instruction to resource it: enhanced due diligence, tighter monitoring, and a testing sample that includes the segment. Exiting the class to avoid that work is a business decision. Recommendation 1 describes a calibration of controls, not a substitute for having them.
FinCEN's AML/CFT Priorities, issued June 30, 2021, name eight threats, in no particular order: corruption; cybercrime, including cybersecurity and virtual currency; foreign and domestic terrorist financing; fraud; transnational criminal organization activity; drug trafficking organization activity; human trafficking and human smuggling; and proliferation financing. FinCEN said not every priority will touch every covered institution, and that incorporation waited on program regulations. The approach is the decision about which of the eight the institution's products, customers, and corridors actually present.
On April 7, 2026, FinCEN proposed an AML/CFT program rule that would make the principle explicit and withdraw its July 2024 proposal. The proposal would require effective, risk-based, and reasonably designed programs, direct more attention and resources to higher risks than to lower ones, and tell examiners and auditors not to replace an institution's risk-based design with a preference of their own. Comments closed on June 9, 2026. The text of 31 CFR 1020.210, last amended in the Federal Register on September 15, 2020, has not been revised to adopt it. The binding standard remains the rule examiners already apply.
Sphinx's agents work the cases a risk-based program produces. They apply the institution's own risk ratings and procedures, review the evidence an analyst would review, and record the basis for each disposition, so a higher-risk file does not leave the same write-up as a lower-risk file. Sphinx reports 87 percent fewer false positives, an 80 percent reduction in case review time, and 98 percent of cases resolved the same day. The approach stays with the institution. An agent does not rewrite the assessment, and it does not retire a control the assessment still requires.
A risk-based approach to AML requires an institution to identify, assess, and mitigate money laundering and terrorist financing risk in proportion to that risk. Higher risk receives enhanced measures, and lower risk may receive simplified measures where the rules allow them. FATF Recommendation 1 sets the international standard, and 31 CFR 1020.210 builds risk-based customer due diligence into the U.S. bank program rule.
No. The BSA/AML risk assessment is the written analysis of products, customers, geographies, and channels. The FFIEC manual calls that written assessment sound practice and not, by itself, a specific legal requirement. The risk-based approach is the set of decisions that analysis produces across due diligence, screening, monitoring, and testing.
Yes, where the rules allow simplified measures and the institution has assessed the risk as lower. FATF's interpretive note to Recommendation 1 bars simplified measures whenever money laundering or terrorist financing is suspected. A low rating can change refresh frequency and file depth, and it does not remove the identification the program rule already requires.
It allows the margin to move, not the floor. Rescreening cadence, supplemental lists, and the order in which hits are worked can follow risk, while targeted financial sanctions still have to be fully implemented where proliferation-financing risk is assessed as lower. A low customer rating is not a reason to drop a required list.
The FFIEC manual sets no fixed testing frequency. Frequency and sample should match the institution's risk profile, with every 12 to 18 months offered as an example and a further test when the risk profile, systems, staff, or processes change. A risk-based test concentrates on the higher-risk products and segments, and the tester's independence does not scale down with the rating.
A bank files a SAR within 30 days of initial detection, or 60 days if no suspect was identified that day.
Payment screening compares a wire, ACH, or SWIFT message with sanctions lists before funds move. It is separate from customer name screening.
Source of funds traces a transfer. Source of wealth traces how net worth was built. When each is required, and what evidence holds.
Automate CIP, screening, UBO resolution, risk rating, and the evidence pack. Source of wealth, high-risk approval, and SAR suspicion stay with a person.
Best compliance software for credit unions has to cover BSA/AML, sanctions, KYC, shared branching, and examiner-ready case files.
What a bank sanctions screening program must include: lists, customer and payment screening, escalation, and examiner records.
How to cut false alerts in transaction monitoring by tuning one scenario at a time, fixing data, and keeping the threshold version.
How to compare UBO mapping tools when a U.S. registry does not return owners: chains, the 25 percent prong, and the control person.
How to set lists, match thresholds, disposition paths, and testing for automated sanctions screening alerts.
What a KYB API returns from a U.S. registry, what it does not, and why banks still collect beneficial owners under CDD.
How compliance teams build, tune, and document transaction monitoring: risk-based scenarios, data quality, and alert decisions.
What to evaluate in AI screening alert tools: triage, false-positive claims, OFAC calibration, and an audit trail you can replay.
What breaks a compliance platform at high alert volume: queue age, rule noise, analyst minutes, and audit reconstruction.
Manual KYB cost covers analyst time, rework, lost onboardings, missed owners, and later audit reconstruction. Corporate reviews average $2,274.
Small fintechs need a full KYB file: entity, owners, control person, refresh, and an audit trail. Cheap checks skip the hard parts.
AML screening is slow because each hit is research: list updates, fuzzy names, weak aliases, missing context, and a written disposition.
What payment processors and payfacs should demand from KYB: sub-merchant underwriting, ownership, and monitoring after the business changes.
KYC false positives start in the name match. FCA tests found 75% detection on slight variants. How list scope and date of birth clear the rest.
What a BSA program must operate: CIP, CDD, SAR and CTR filings, sanctions screening, and risk-based controls.
How to backtest AML rules on historical data, run shadow mode and champion-challenger in production, and document results for model risk management.
How entity resolution and graph analytics identify beneficial owners: probabilistic matching, blocking, indirect ownership math, cycles, registry limits.
Integration patterns, data mapping, cutoffs, sandbox and UAT, reconciliation, and post-go-live failures when connecting AML and KYC tools to a bank core.
Compliance orchestration routes data, decisions, and cases across KYC, KYB, sanctions, and monitoring tools. Architecture patterns and what to evaluate.
Senate PSI report: 84% of Iran-linked sanctioned wallets ran on USDT. Why a post-designation freeze is not a sanctions program, and what regulators ask.
Brazil's betting ban pushes 30M bettors to illegal sites. What Pix monitoring teams will see, SPA Ordinance 2,750's red flags, and why alert queues flood.
MP 1,394 article by article: CPF refund lists, the 7-day bank restitution window, SPA reporting, Caixa fallback, and the pending Central Bank Pix block.
Who counts as an MSB, FinCEN Form 107 registration, state licensing, the $2,000 SAR threshold, agent oversight, and what IRS BSA examiners find.
The OFAC SDN List names blocked persons, vessels, aircraft, and crypto addresses. How screening works, what a true hit requires, and what a miss costs.
What the crypto Travel Rule requires of VASPs: FATF R.16, FinCEN's $3,000 rule, EU and UK thresholds, self-hosted wallets, IVMS 101, and the sunrise gap.
How bust-out fraud works, how it differs from default and account takeover, the signals and features that catch it, and why the loss ends up as a SAR.
How to run an enterprise BSA/AML risk assessment: FFIEC categories, inherent vs. residual risk, refresh triggers, examiner criticisms, program linkage.
How fuzzy name matching works in sanctions screening: Levenshtein, Jaro-Winkler, phonetic keys, OFAC's own scorer, threshold trade-offs, and validation.
Placement, layering, and integration: the techniques, transaction-data signatures, and controls at each stage, and why real schemes break the model.
CIP is the BSA identity program at account opening under 31 CFR 1020.220.
A Currency Transaction Report is FinCEN Form 112 for cash over $10,000 in one business day. Covers aggregation, exemptions, and how CTRs differ from SARs.
What FinCEN 314(a) information sharing is: government-to-institution searches, 14-day match reporting, and how it differs from voluntary 314(b).
BSA officer responsibilities go beyond a board title: designation, independence, SAR authority, board reporting, staffing, and what examiners test.
Wire fraud detection for banks: known-number callbacks, beneficiary checks, mule holds, and 24-hour IC3 recall. IC3 reported $20.877B in 2025 losses.
BSA independent testing: independence, risk-based frequency, sampling, board reporting, and what OCC examiners expect after Bulletin 2025-37.
How banks evaluate AML vendors under OCC and FFIEC third-party risk rules, including residual BSA risk for processors, screening, BPO, and model vendors.
How banks and credit unions detect altered, counterfeit, forged, and duplicate checks: typologies, detection layers, Reg CC holds, and SAR key terms.
What an AML lookback review is, what triggers one, how regulators scope it, what TD Bank-scale lookbacks cost, and how automation changes the economics.
Shell company red flags at onboarding and in transaction activity, how to investigate a suspected shell, and what detection tooling needs to do.
The five pillars of an AML compliance program, what examiners test under each, common exam findings, and how FinCEN's 2026 proposed rule reframes them.
How transaction monitoring rule tuning works: ATL/BTL testing, sensitivity analysis, segmentation, cadence, and the documentation examiners expect.
How banks detect account takeover fraud: attack vectors, the signals that give ATO away, SAR and FFIEC obligations, and how to evaluate detection tools.
Customer risk rating in AML: the five factors behind the score, static vs dynamic rating, how scores drive EDD and monitoring, and what examiners expect.
FinCEN human trafficking red flags for banks: labor vs sex trafficking footprints, funnel accounts, payroll absences, SAR filing rules, and forced criminality typologies.
How FinCEN 314(b) information sharing works after the June 2026 fact sheet: safe harbor conditions, fraud coverage, real-time sharing, enrollment, and the renewal trap.
APP fraud prevention across UK, EU and US rules: what Confirmation of Payee fixes, what it cannot, and why receiving-side mule detection only got built when liability shifted.
What the GENIUS Act requires of stablecoin issuers: reserves, BSA program, seize and freeze capability, Travel Rule, MiCA comparison, and the secondary market gap.
Why synthetic identities pass CIP, how the credit bust-out lifecycle works, which signals actually detect them, and why the risk concentrates in super prime.
How to build an AML QA program: sampling design, scorecards, error taxonomy, 2026 enforcement actions, and what changes when AI agents disposition alerts.
How banks detect pig butchering scams: FinCEN red flags, the trial-transaction signal, receiving-side mule controls, and why 78% of victims defend the payment.
Eight financial crime, compliance and fintech conferences in fall 2026. Dates, cost, audience, date conflicts and which deserves your travel budget.
ACAMS Assembly Las Vegas 2026 runs Sept 29-Oct 1 at ARIA. Theme, agenda, 15 credits, the free CAMS seminar most attendees miss, and how to prepare.
XLoD Global New York 2026 runs Sept 24 at the Javits Center. Streams, speakers, who attends, how to prepare and what to ask vendors.
Money20/20 USA 2026 runs Oct 18-21 at The Venetian, Las Vegas. Content pillars, costs, schedule, who it suits and how to prepare.
FinovateFall 2026 runs Sept 9-11 at the Marriott Marquis Times Square, NYC. Demo format, agenda, compliance sessions, costs and how to prepare.
Global Anti-Scam Summit America 2026 runs Sept 2-3 at Pier 48, San Francisco. Dates, ticket tiers, agenda focus areas, who attends and how to prepare.
Stablecon 2026 runs Sept 9-11 at National Harbor, Maryland. Dates, venue, agenda, GENIUS Act context, who attends and how to prepare.
Elder financial exploitation detection separates elder scams from theft by trusted persons. FinCEN SAR rules, red flags, and how to evaluate a program.
Sanctions evasion red flags across six typologies: front companies, ownership obfuscation, transshipment, AIS manipulation, and trade misdescription.
Structuring in banking explained: 31 U.S.C. 5324, the $10,000 CTR threshold, red flags, SAR obligations, and how to build defensible detection.
How sponsor banks supervise fintech and BaaS partners: third-party risk expectations, who owns BSA/AML, ledger access, and oversight cadence.
How correspondent banks assess respondent institutions: FATF Rec 13, the Wolfsberg CBDDQ, nested accounts and Section 312 enhanced due diligence.
Trade-based money laundering moves criminal value through misinvoiced trade. The core techniques, red flags in trade finance, and how to build controls.
What AML model validation requires after SR 26-2 replaced SR 11-7: scope, threshold tuning, outcomes analysis, and the evidence examiners expect.
Compare API-first compliance platforms that embed screening, monitoring, and verification into product workflows. Covers latency, pricing, and integration patterns.
Compare business onboarding software for banks, credit unions, and fintechs. Covers KYB verification, UBO mapping, screening, and risk-based due diligence workflows.
Head-to-head comparison of transaction monitoring software pricing models, key features, and ROI drivers for banks and fintechs in 2026.
How banks detect fraud in real time using rules, behavioral analytics, and network intelligence. Covers detection architecture, false positive management, and regulatory expectations.
Compare compliance automation platforms for fintechs: financial crime compliance (AML, KYC) and security compliance (SOC 2, ISO 27001). Evaluation criteria and pricing.
Compare the best financial crime prevention software for banks and fintechs in 2026. Covers unified platforms, AI-native challengers, and key evaluation criteria.
Compare KYB platforms for regulated financial institutions including LexisNexis, Middesk, Alloy, Trulioo, GBG, and Sumsub with audit trail and compliance evaluation criteria.
A practical guide to automating AML and KYC compliance processes covering alert triage, screening, onboarding, and SAR filing with evaluation criteria and common pitfalls.
Compare the top KYB automation platforms for fintech in 2026. Covers Middesk, Sumsub, Alloy, Persona, Trulioo, and more with pricing, coverage, and evaluation criteria.
Five practical strategies to cut business verification time including parallel checks, API-first data, automated UBO traversal, risk-based routing, and perpetual monitoring.
How the OFAC 50 Percent Rule works, including indirect ownership, aggregation across sanctioned owners, and documenting screening decisions.
A mule account moves fraud proceeds through the banking system. Learn the detection signals, analyst investigation steps, and SAR reporting requirements.
Credit unions face document fraud at three unique entry points: member onboarding, indirect lending, and shared branching. How to evaluate detection at credit union scale.
AI-generated document fraud is surging. Most onboarding platforms rely on OCR and template matching that miss synthetic forgeries. How multi-layer verification catches what legacy checks cannot.
A guide to the four types of document fraud in banking and the five-layer detection framework compliance teams need to catch AI-generated fakes.
Community banks face the same BSA/AML requirements as institutions 10x their size. Learn what to look for in AML technology, how FinCEN's effectiveness rule changes the game, and how to evaluate solutions for $1B-$10B institutions.
What BSA examiners evaluate at community banks in 2026: risk assessment currency, TM tuning rationale, SAR narrative quality, CDD documentation, and how AI audit trails change the exam conversation.
Ranked comparison of the top crypto compliance software in 2026 covering Chainalysis, TRM Labs, Elliptic, ComplyAdvantage, Crystal Intelligence, Merkle Science, Notabene, and Sphinx.
UBO mapping automation replaces manual ownership tracing with systems that reconstruct corporate ownership graphs programmatically. Learn how to evaluate tools.
Ranked comparison of the best SAR filing software in 2026 covering Hummingbird, Abrigo, NICE Actimize, Verafin, Lucinity, Unit21, Flagright, and Sphinx.
Ranked comparison of the best transaction monitoring software in 2026 covering NICE Actimize, SAS, Feedzai, Hawk AI, ComplyAdvantage, Verafin, Unit21, Quantexa, and Sphinx.
Ranked comparison of the best sanctions screening software in 2026 covering Dow Jones, Refinitiv, ComplyAdvantage, NICE Actimize, LexisNexis, Napier AI, Alessa, and Sphinx.
PEP screening identifies politically exposed persons, their family members, and close associates to apply risk-based enhanced due diligence under FATF and AML regulations.
Adverse media screening searches public sources for risk signals about customers. Learn what regulators require and how to evaluate a screening program.
Ranked guide to the best compliance case management software in 2026. Covers evaluation criteria, platform categories, regulatory requirements, and how to choose.
Financial crime detection identifies suspicious activity after the fact. Prevention stops it before funds move. Here is how to evaluate the right balance for your compliance program.
Evaluate business onboarding automation software for banks. Covers KYB verification, beneficial ownership, sanctions screening, and what to look for in a platform.
What banks must verify, monitor, and document under FinCEN's CDD Rule — including the 2026 beneficial ownership changes and how to evaluate your program.
Compare risk assessment software for banks and fintechs. Covers AML risk scoring, regulatory alignment, audit trails, and what compliance teams should evaluate.
Modern fraud detection layers ML scoring, behavioral biometrics, and graph neural networks to catch fraud in milliseconds while reducing false positives.
Perpetual KYC (pKYC) replaces periodic reviews with continuous, event-driven monitoring. Learn how it works, what triggers reviews, and what it takes to implement.
Compliance officer burnout is a systems problem, not a people problem. Learn how AI case-level automation removes repetitive volume and makes the role sustainable.
The AML efficiency gap separates compliance activity from risk reduction. Learn how outcome-based measurement and lower false positive rates close it.
Learn how to write SAR narratives that law enforcement can act on. Covers FinCEN's five-W framework, October 2025 guidance changes, and common mistakes to avoid.
FRAML merges fraud and AML into one program. Learn why 93% of mid-market banks are converging, the cost savings, and how to evaluate readiness.
FinCEN's 2026 proposed rule replaces process-driven AML compliance with an effectiveness-based standard. Learn the two-pronged framework and how to prepare.
Ranked comparison of the best fraud detection platforms in 2026 covering Feedzai, NICE Actimize, Featurespace, SAS, and Hawk AI with an evaluation framework.
Ranked guide to the best compliance software for financial services in 2026, covering AML, KYC, KYB, and security compliance platforms.
UBO identification traces beneficial ownership through corporate layers to find the natural persons who own or control an entity.
Ranked comparison of the best AML software in 2026 covering ComplyAdvantage, NICE Actimize, LexisNexis, Hawk AI, TRM Labs, Alloy, and Sphinx.
Screening alerts take 30-45 minutes each, with 85-90% being false positives. Four capabilities cut review time without compromising audit readiness.
Enhanced Due Diligence (EDD) applies deeper scrutiny to high-risk customers. Covers triggers, requirements, source of funds verification, and the operational cost of EDD programs.
KYB (Know Your Business) verifies business entities, ownership structures, and beneficial owners. Guide covering FinCEN CDD Rule, FATF Rec 24, and evaluation criteria.
KYC verifies individuals, KYB verifies business entities and their beneficial owners. A comparison of scope, complexity, cost, and regulatory drivers.
Screening alert backlogs are a design problem, not a staffing problem. Most systems were built to flag matches, never to resolve them at scale.
AML transaction monitoring detects suspicious financial activity through rules and behavioral models. Covers detection methods, alert investigation, SAR filing, and false positives.
U.S. crypto AML compliance: regulators are no longer satisfied with policy documents. They want evidence that the program actually ran.
Compare the best KYC software in 2026. See top vendors, key strengths, and the compliance gaps buyers should evaluate before choosing.
Learn what actually reduces AML false positives - data quality, context, explainability, and automation - and how to spot vendor theater.
Global compliance automation that scales seamlessly across borders.
Try another keyword or explore a different topic.