
How to Spot a Fake Credit Card Statement
How to spot a fake credit card statement used for proof of address, debt verification, or source of funds: edited balances, broken math, file checks.
TL;DR: A fake crypto exchange statement is an account statement, transaction history, or CSV export that misstates what an exchange account held, traded, or withdrew, usually to explain a large fiat deposit as crypto gains. The FBI's IC3 logged 181,565 complaints involving cryptocurrency in 2025, with $11.4 billion in reported losses, and many of those scams showed victims fake profits on fake platforms. A clean layout proves little. The withdrawal on the blockchain, the exchange's own export, and the file's history are what separate a real statement from an edited one.
A crypto exchange statement is the record a centralized exchange produces for one account: deposits, trades, fees, withdrawals, and balances over a period. It reaches a bank, lender, or onboarding team when a customer says that money arriving in fiat came from crypto. That claim is a source of funds question for one deposit, and often a source of wealth question for the whole balance sheet.
The paperwork has rules. Fannie Mae's Selling Guide accepts virtual currency for a down payment, closing costs, or reserves only when there is documented evidence it was exchanged into U.S. dollars and held at a U.S. or state regulated financial institution, verified in dollars before closing. When a large deposit may have come from crypto, the lender must document that the funds originated from the borrower's virtual currency account. Under Fannie Mae's depository account rules, a large deposit is a single deposit above 50% of total monthly qualifying income. Crypto proceeds clear that line easily.
In the UK, the Law Society of England and Wales' practice advice on bitcoin and property tells firms to trace the original money into the exchange, confirm the investment produced the proceeds, and confirm those proceeds landed in the account funding the purchase. Every step of that trace is a document someone can alter.
Fake exchange statements arrive in three production classes. Edited-after-creation starts with a real statement PDF or a real CSV export and changes a balance, a realized gain, a withdrawal amount, or the account holder's name after the exchange produced the file. Generated-from-scratch starts from a template or a screenshot of an exchange's interface and invents the account. The third class is specific to crypto: a genuine file from a platform that is not a real exchange. The FBI's IC3 2025 report put cryptocurrency investment fraud at $7.2 billion in reported losses, the largest category for Americans, and describes scam platforms that show victims fake profits. A statement from that platform is unaltered and still worthless.
Exchange branding, a familiar color scheme, and a tidy table catch a statement made by someone who never logged into the exchange. They do not catch an altered real export. Every major exchange lets a customer download a statement, so a genuine starting file is always one click away.
CSV exports deserve special suspicion. A CSV is plain text with no fonts, no layout, and no producer field, so it carries almost no production story. Opening it in a spreadsheet and saving it again erases whatever trace remained. A transaction history submitted only as a CSV, or a CSV re-rendered into a PDF, has removed the evidence a document check would read. Screenshots of an exchange dashboard sit in the same category. Several exchanges accept screenshots for their own source of funds reviews, which is why they circulate, but a screenshot is a picture of a balance, not a record of one.
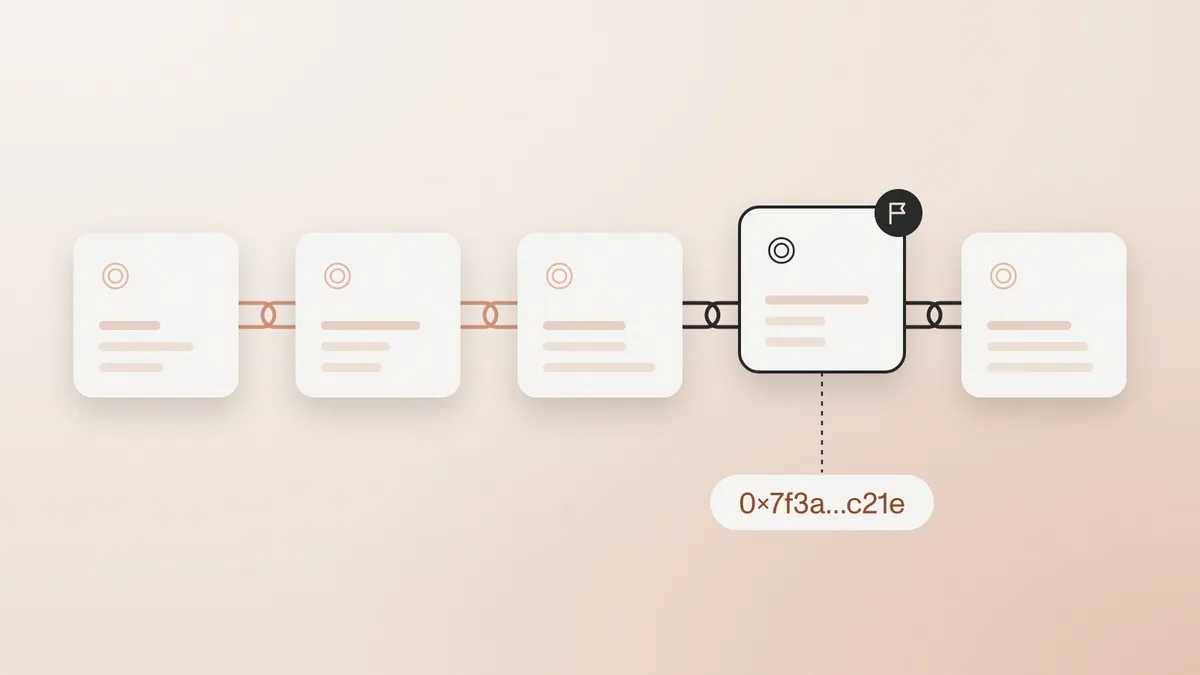
The tells that survive a competent edit connect the statement to records the customer does not control. The blockchain is the strongest of these. Deposits to and withdrawals from an exchange settle on-chain, with a transaction hash, an amount, a timestamp, and destination address that anyone can look up. Trades inside the exchange do not settle on-chain; they live on the exchange's internal ledger. A statement can therefore be checked against the chain at its edges, where crypto came in and went out, and against market data in the middle.
A real transaction hash with the account holder's name changed on the statement clears the explorer check. Who controls the address is a separate question from whether the transfer happened.
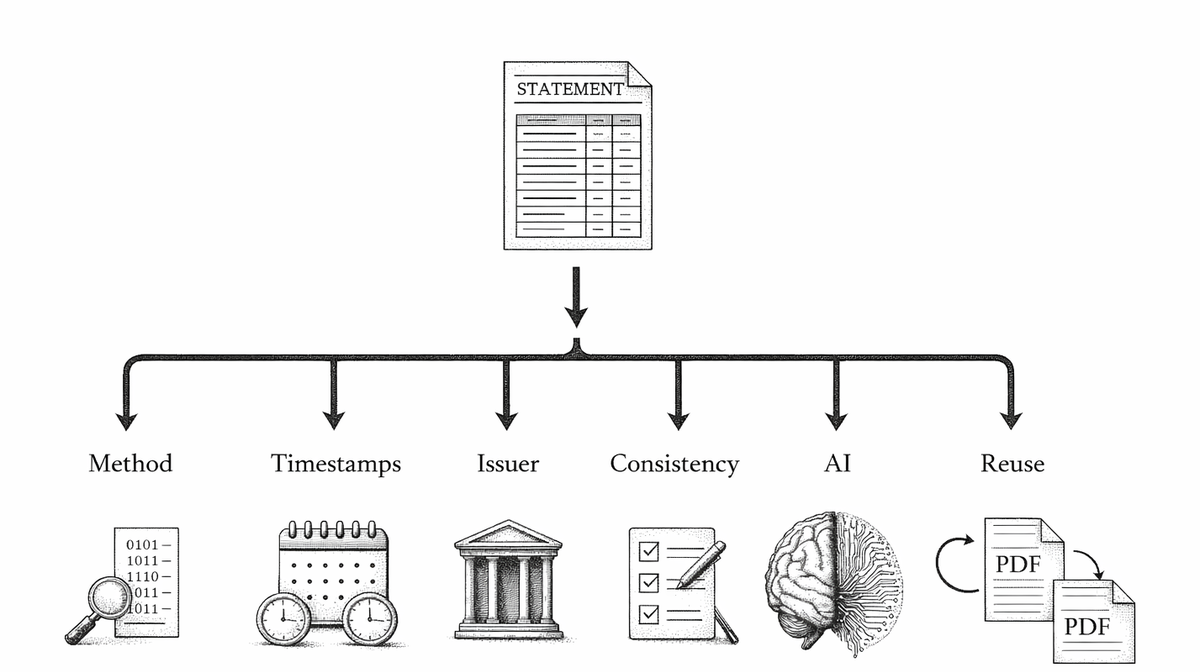
Detection that holds up reads the file's story first, then the account's story, through six classes of signal.
Production method asks how the bytes were made. An exchange's statement service produces PDFs through a consistent pipeline, and a file last saved in a desktop editor, printed to PDF from a browser, converted from an image, or rendered from a spreadsheet carries a different one. Edited-after-creation and generated-from-scratch are separate findings, because a genuine export can sit underneath a later save. Timestamp trail asks whether creation, modification, and upload line up with the statement period. A statement for a period that ended last month, created last month, and modified yesterday needs an explanation.
Issuer matching asks whether the named exchange exists, is registered where it claims to be, and produces statements that look like this one: same fields, same account identifiers, same fee lines, same rounding of asset quantities. A platform with no regulator record and no public footprint is the scam-platform case, where the file is authentic and the issuer is the problem. Consistency then tests the numbers against outside records. Balances should roll forward. Trade prices should fall inside the market range at the stated time. Withdrawal fees should match the network and the exchange's schedule. Each withdrawal hash should show the same asset, amount, and time on-chain, and the fiat withdrawal should appear as a credit on the customer's bank statement with the exchange or its payment processor named as the sender.
Model artifacts ask whether generative tooling left traces a viewer does not show, from rendering patterns to text layers that disagree with the visible page. The AI-generated PDF guide covers that class in detail. Recycled patterns ask whether this exact file, this transaction hash, this wallet address, or this statement template has appeared on another customer. A transaction hash belongs to one transfer. The same hash on two unrelated applicants is a finding no single reviewer would notice.
A flagged exchange statement is a hold, pending evidence the customer cannot edit. Rejecting on a gut feeling turns away customers who really did make money in crypto. Accepting on layout passes the edited file. The middle path asks for records that come from somewhere other than the customer's downloads folder.
Start with the chain. Ask for the transaction hashes of the withdrawals that funded the deposit and look them up on a public block explorer. Confirm the asset, amount, time, and the destination address. Where the customer claims a self-hosted wallet, the Law Society of Scotland's guidance on crypto source of funds describes asking the client to send a trivial amount to or from the wallet to prove control, often called a Satoshi test. A blockchain analytics scan can add exposure to mixers or sanctioned addresses, which belongs in the AML review and not in the document verdict.
Then go back to the issuer. Ask for a fresh statement downloaded during a screen share, a statement emailed from the exchange's own domain, or read-only API access if the institution supports it. Request the full history back to the first fiat deposit, because source of wealth depends on how the position was funded, not only on how it was sold. Read the exchange statement against the bank statement that shows the original purchase and the bank statement that shows the proceeds landing. A brokerage statement used to explain the same wealth gets the same treatment.
Keep the original file. Leave the specific failed signal out of any message to the customer, and document the gap in the file: the field, the record it failed against, and what was requested next. Check a document in the Watchdoc playground before the follow-up request goes out, so the x-ray is on file when the new statement arrives. The first file is free, and no email is required.
Watchdoc scores the file and shows the x-ray across production method, timestamp trail, issuer matching, consistency, model artifacts, and recycled patterns. Published figures are a 94.3% correct verdict, 2.8x more forgeries caught, clean files cleared in under 28 seconds, and a review path 54% less expensive, across 1 million documents processed, at $0.45 per document with no seats and no platform fee. The block explorer confirms the transfer. The Watchdoc playground confirms the file, with a 50-document free tier. Teams building the wider control set can pair both with the steps in building a crypto AML compliance program and the cross-document review in document fraud in banking.
Check the file and the account separately. The file should show an exchange's own production pipeline and timestamps consistent with the statement period. The account should reconcile: balances roll forward, trade prices sit inside the market range, and each withdrawal hash appears on-chain with the same amount and time.
Deposits to and withdrawals from an exchange can be verified on-chain by transaction hash, amount, time, and address. Trades inside a centralized exchange cannot, because they settle on the exchange's internal ledger. On-chain data proves a transfer happened, not who controls the address, so a Satoshi test or the exchange's own records still matter.
A CSV export is plain text with no production metadata, so it is easy to alter and hard to authenticate. Treat it as a summary that must reconcile with on-chain withdrawals, a PDF statement, and the bank account that received the proceeds. On its own, it is weak evidence.
Fannie Mae accepts virtual currency for a down payment, closing costs, and reserves once it has been exchanged into U.S. dollars, held at a U.S. or state regulated financial institution, and verified in dollars before closing. The lender must document that a large deposit originated from the borrower's virtual currency account. Crypto cannot be used for the earnest money deposit.
Scam investment platforms show victims fake profits and produce statements that look authentic because the platform made them. Check that the exchange is registered with a regulator, has a public footprint, and pays out to a bank account in its own name. A genuine file from a fake issuer fails issuer matching even when nothing in the PDF was edited.
How to spot a fake credit card statement used for proof of address, debt verification, or source of funds: edited balances, broken math, file checks.
Spot a fake W-8BEN by reading foreign status, the treaty claim, and the file. The IRS publishes a blank and does not certify the form.
How to spot a fake partnership agreement: edited partner lists, signature blocks never executed together, and no state filing for a general partnership.
How to spot fake corporate bylaws: rules that contradict the articles, adoption before incorporation, and a template reused across companies.
How to spot a fake stock certificate offered as KYB ownership evidence, when the ledger matters more than the vignette.
A Schedule K-1 reports a partner's share of income. Capital-account math, form year, and an IRS transcript catch edited and generated fakes.
A fake 1099 is an information return edited after creation or generated from scratch. Match it to the IRS wage and income transcript.
How to spot a fake employment verification letter: edited versus generated files, the tells that fail, and six checks on the file.
Spot a fake mortgage statement by confirming principal, amount due, due date, and rate with the current servicer.
Spot a fake W-9 by matching the line 1 name and TIN. The IRS publishes a blank form and does not seal a completed one.
Spot a fake merchant statement by rebuilding amount processed from the fee lines and confirming the merchant ID with the processor.
Spot a fake DBA certificate in the county index: file number, registrant, and expiration. A filing is not good standing.
Spot a fake board resolution by checking that the certifier is not the empowered signer and that the resolution date comes first.
Spot a fake certificate of incumbency by checking the certifier and the state's officer list. A seal does not prove the offices.
How to spot a fake brokerage statement used as proof of assets, and why file history beats a clean layout.
How to spot fake articles of organization by matching the file number and filing receipt to the state record before the account opens.
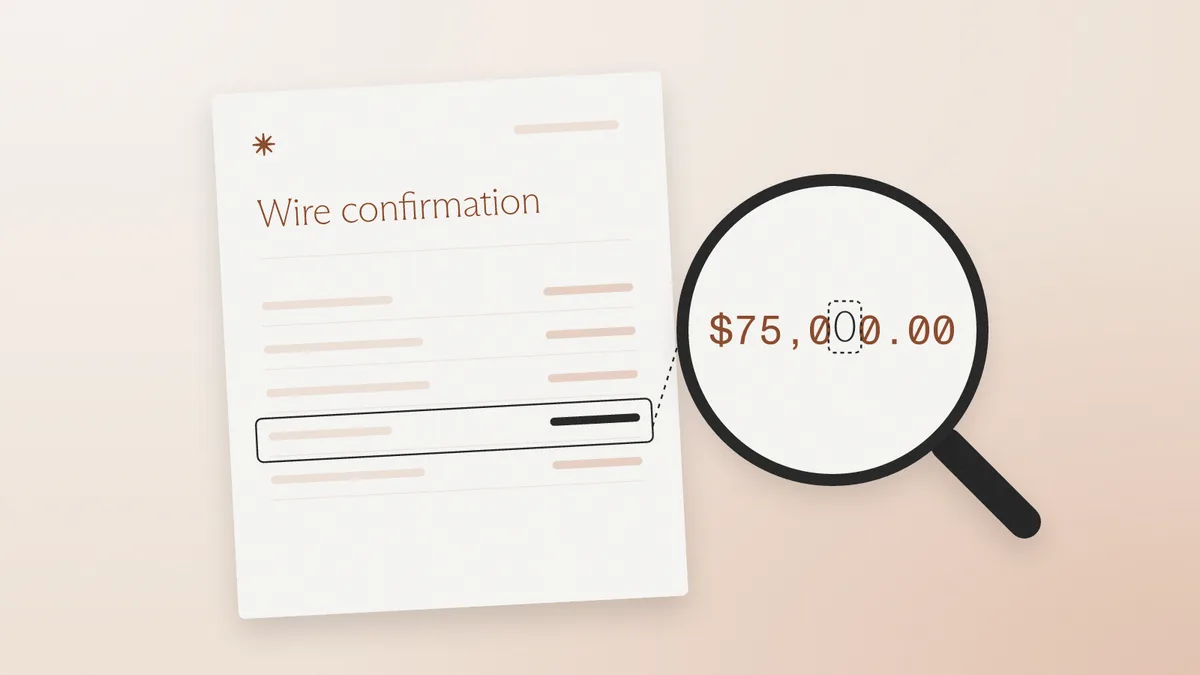
A wire confirmation is a claim that money moved. Edited and generated payment advice fail file checks. The posted credit is the proof.
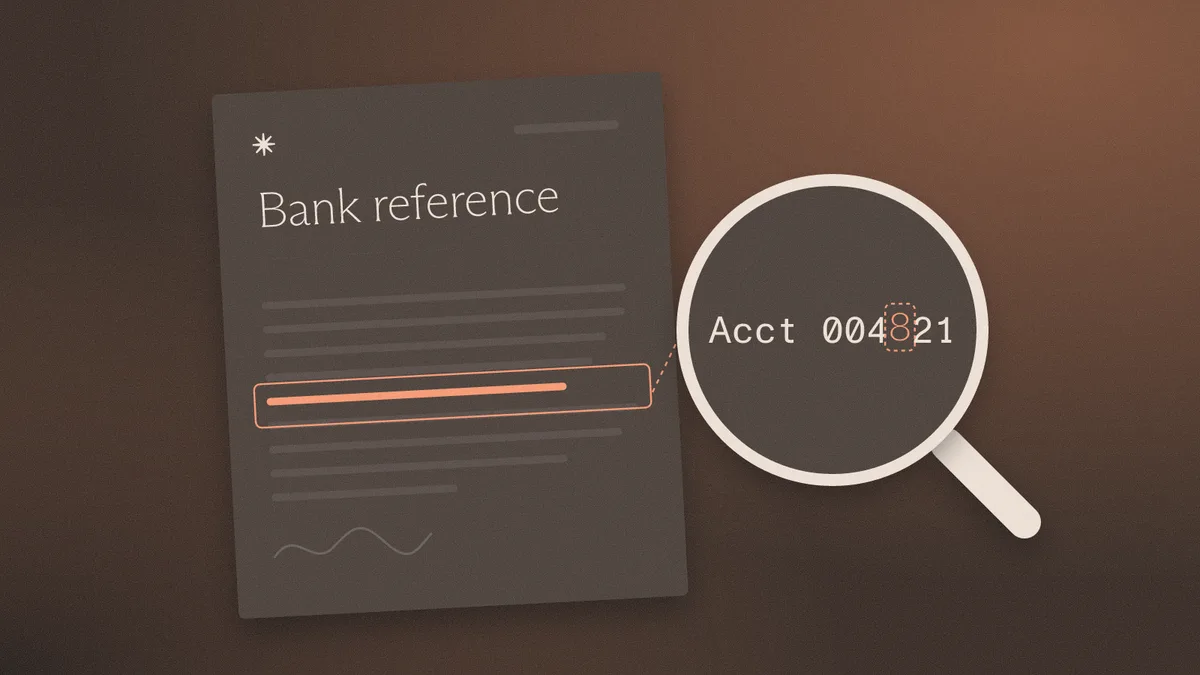
How to spot a fake bank reference letter: the relationship claim, the signatory, and the edit history. Letterhead is cheap to copy.
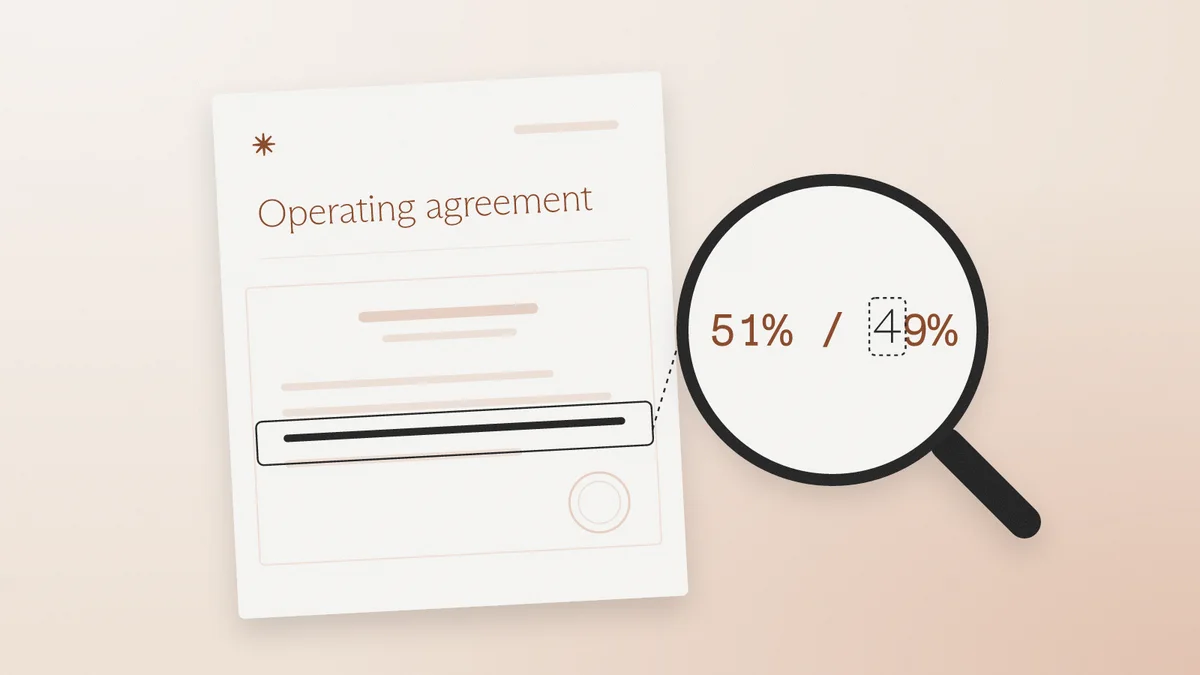
How to spot a fake operating agreement in KYB: edited member schedules, swapped signature pages, and ownership that does not match the file.
Spot a fake certificate of good standing by checking the as-of date, file number, and post-download edits.
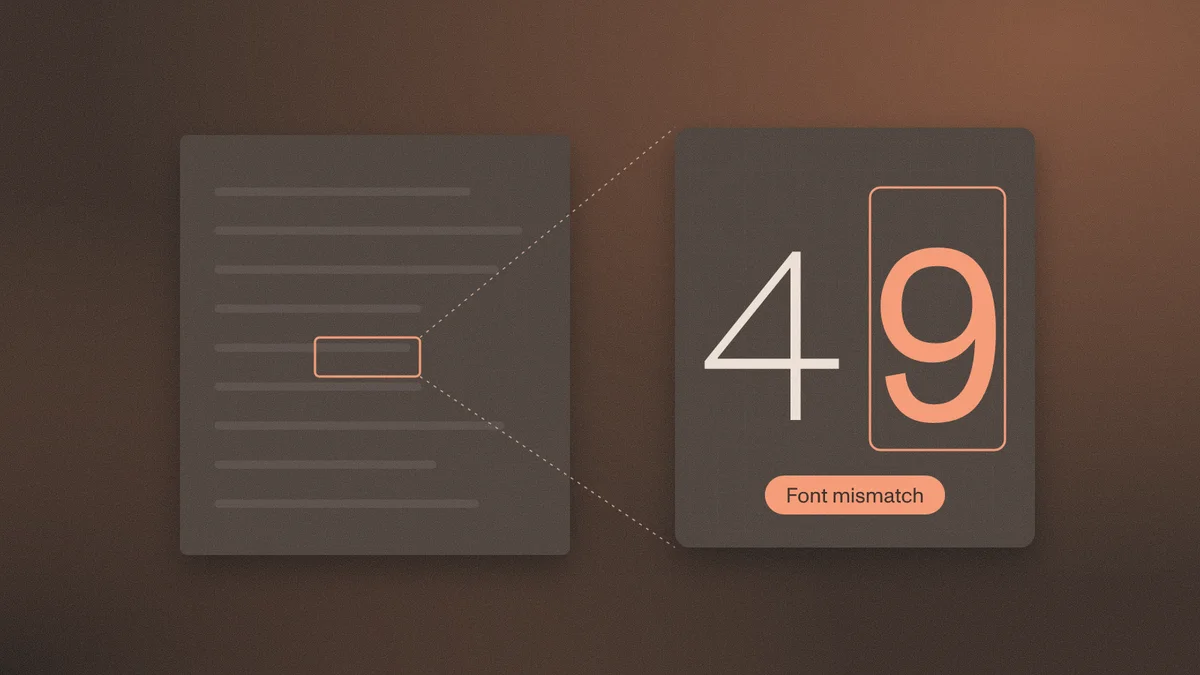
How to spot a fake voided check using file history, routing match, and account control. A VOID mark misses edited and generated files.
Verification reads the page and matches the applicant. Fraud detection reads the file. What each misses, how to evaluate each, and when you need both.
PDF metadata analysis for fraud detection: Info dictionary, XMP, timestamps, producer strings, incremental updates, and what each can and cannot prove.
How to spot fake financial statements in SMB lending and KYB: inflated revenue, fake auditor letters, 4506-C and bank reconciliation, six file checks.
How to spot a fake certificate of insurance: why an ACORD 25 confers no rights, the tells that survive, carrier and NAIC lookups, and the six file checks.
How to spot a fake lease agreement in KYC, mortgage, and KYB review: landlord, date, rent, and disclosure tells, plus the six file checks that settle it.
How to spot a fake proof of funds letter in lending, real estate, and escrow: the tells that work, the six file checks, and how to verify with the bank.
How to spot a fake EIN confirmation letter: what a real CP 575 or 147C contains, the tells that survive, IRS TIN Matching limits, and the six file checks.
How lenders and onboarding teams spot fake 1040s, W-2s, and IRS transcripts: line-item tells, edited vs generated files, and the Form 4506-C break-test.
How to spot a fake invoice in factoring, trade finance, and AP: the tells that still work, the six file checks, and the debtor break-test that settles it.
Should compliance teams accept screenshots of bank statements? What a flattened PDF loses, which fraud checks still work on images, and how to set policy.
Explainable document forensics shows where a file was altered, what it said before, and how the examiner knows. Why a fraud score alone fails audit.
How KYC, KYB, rental, and lending teams spot fake utility bills used as proof of address: edited vs generated files, tells that work, six file checks.
How fake document templates and template farms work, why template-made files have no issuance history, and how to detect them in KYC and lending.
Serial document reuse detection catches one statement, stub, or ID recycled across unrelated applicants. Why single-file review misses it.
Loan document fraud detection tests bank statements, pay stubs, and tax docs as a package — the red flags underwriters miss on visual review.
KYB document fraud detection checks certificates, registry extracts, and proof of address as files. Visual review misses edited-after-creation PDFs.
Document fraud statistics from FinCEN, FBI IC3, and FTC — and what those figures miss about edited PDFs, counterfeit templates, and file-level detection.
How to spot a fake certificate of incorporation in KYB: registrar mismatch, edited seals, generated COIs, and serial reuse. Visual review is not enough.
How to detect an AI-generated PDF using metadata, empty Producer strings, model artifacts, and the file history visual review misses.
How lenders and onboarding teams spot fake pay stubs: edited vs generated files, deposit cross-checks, and what visual review misses.
How to spot a fake bank statement: edited-after-creation vs generated-from-scratch, which visual tells still work, and how file history exposes forgeries.
Try another keyword or explore a different topic.